01
Who they are
Willie Hutch Jones Educational and Sports Programs, or WHJESP, is a nonprofit that has served Buffalo since 1984. Willie Hutch Jones founded it after retiring from professional basketball, together with Leroi Johnson and the late Bernard Mitchell.
WHJESP gives under-served young people free access to sports, wellness programs, and STEAM projects, which stands for science, technology, engineering, arts, and math. The work is paid for by individual donors and local sponsors, so the website's main job is fundraising.
Visit whjesp.org
02
The issue

The website was not set up to raise money. Donating and sponsoring were single pages with no follow-up. Sponsors got little visible credit for their support, which matters when it is time to renew.
The site also had serious security problems left behind by earlier developers. The theme, which controls how a WordPress site looks and works, had critical vulnerabilities. A paid plugin had been installed from a pirated copy. An error log sat in a public folder. WordPress itself was two major versions out of date.
Visitors could not see any of this, but it put an organization that accepts donations online at risk.
03
How we resolved it

We worked on two things at the same time: fundraising and security.
For fundraising, we built the pages the organization needed to bring money in.
- A donation flowA dedicated giving page with a confirmation step, so donors get an acknowledgment instead of being dropped back on the homepage.
- Sponsorship tiersA sponsorship page that spells out what each level includes.
- Sponsors on every pagePlatinum and Gold sponsors appear in a strip across the whole site, not on one page.
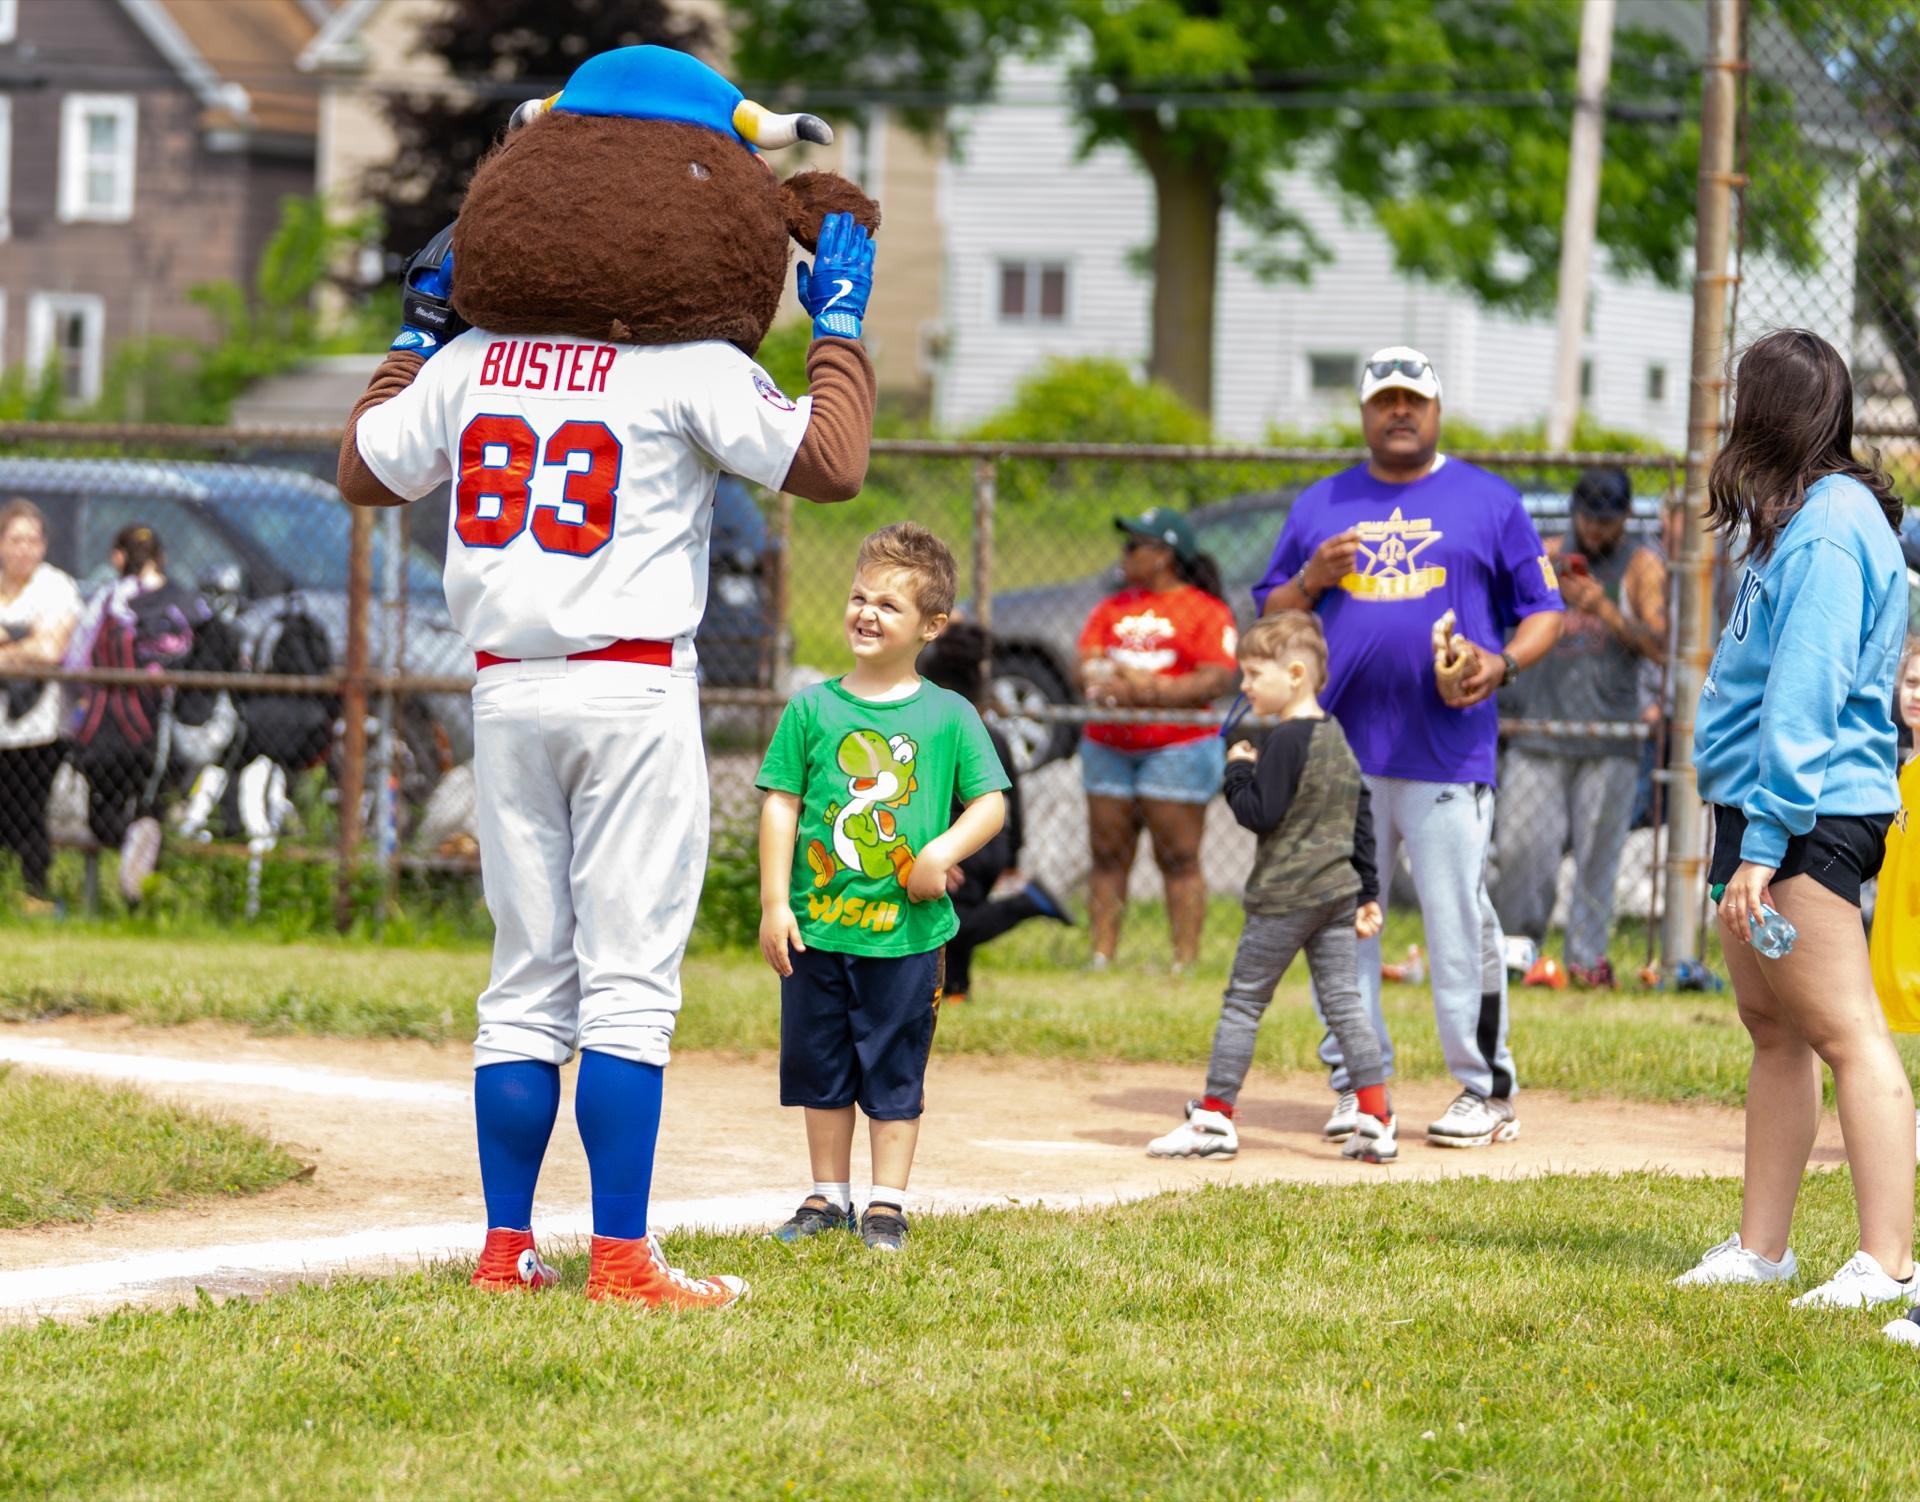
- Program pagesPages for the programs, a Project Play baseball and softball page, and a S.T.E.A.M. Fair page that staff can update each year instead of rebuilding.
For security, we fixed the problems the site had inherited.
- Vulnerabilities closedWe fixed three types of security flaw in the theme: injection, cross-site scripting, and unsafe file inclusion. These are the kinds of flaw that can let an attacker read a site's database or run their own code on it.
- Unsafe files removedWe removed the pirated plugin, the exposed error log, and an old backup file left in a public folder.
- Software updatedWe brought WordPress up to date and removed six plugins nobody was using.
- Server locked downWe added security headers, blocked access to sensitive folders, limited the database to connections from the server itself, and stopped code from running in the uploads folder.
We also made the site faster, using a Lighthouse audit as the guide. Lighthouse is a standard test of page speed and quality.